
Cybersecurity researchers have uncovered an advanced cyber espionage operation aimed at Linux systems supporting government organizations and state-linked infrastructure. Active between October 2025 and April 2026, the campaign has been designated CL-UNK-1211, reflecting an unidentified threat cluster with an unknown primary objective.
What sets this operation apart is the apparent use of artificial intelligence tools, including large language models (LLMs), to help create malicious scripts and automate portions of the attack workflow. Investigators believe the threat actors leveraged AI-generated code to accelerate reconnaissance, persistence, and data theft activities.
According to researchers, the attackers focused heavily on Linux environments, conducting extensive network discovery while maintaining long-term access to compromised systems. Their primary goals appeared to include gathering intelligence, extracting sensitive databases, and accessing government email accounts, potentially to facilitate further compromise of social media and online service accounts.
The campaign relied on a diverse toolkit that combined open-source software, custom-developed backdoors, web shells, and stealth techniques. To evade detection, the attackers attempted to deactivate security products, erase system logs, and even planted misleading artifacts designed to make the activity appear as a legitimate penetration test or red-team exercise.
Researchers also discovered multiple PHP and shell-based malware components that displayed characteristics suggesting they were generated or heavily assisted by AI systems. Rather than containing conventional developer comments, several scripts included conversational explanations and step-by-step reasoning describing how the code functioned, indicating the output may have been copied directly from an AI assistant or deployed by an autonomous AI agent.
To preserve access within victim environments, the threat actors deployed both custom and publicly available PHP web shells that served as persistent backdoors. Once inside, they harvested credentials through several techniques, including replacing user .bashrc files with malicious versions that captured passwords, injecting credential-stealing code into PHP authentication pages, and searching configuration files and command histories for exposed email, SMTP, and database credentials.

A key component of the operation was SysGoRAT, a custom remote access trojan written in Go and capable of running on both Windows and Linux systems. The malware supports multiple persistence mechanisms and establishes communication with a hard-coded command-and-control server over WebSocket connections. Once active, SysGoRAT can execute arbitrary commands, provide interactive shell access, capture screenshots, exfiltrate files, browse directories, create network proxies, and maintain long-term remote control of infected devices.
The attackers further enhanced their stealth by deploying in-memory reverse shells, allowing malicious activity to occur without leaving traditional malware artifacts on disk. They also targeted email infrastructure directly, examining mail directories to identify potentially valuable communications.
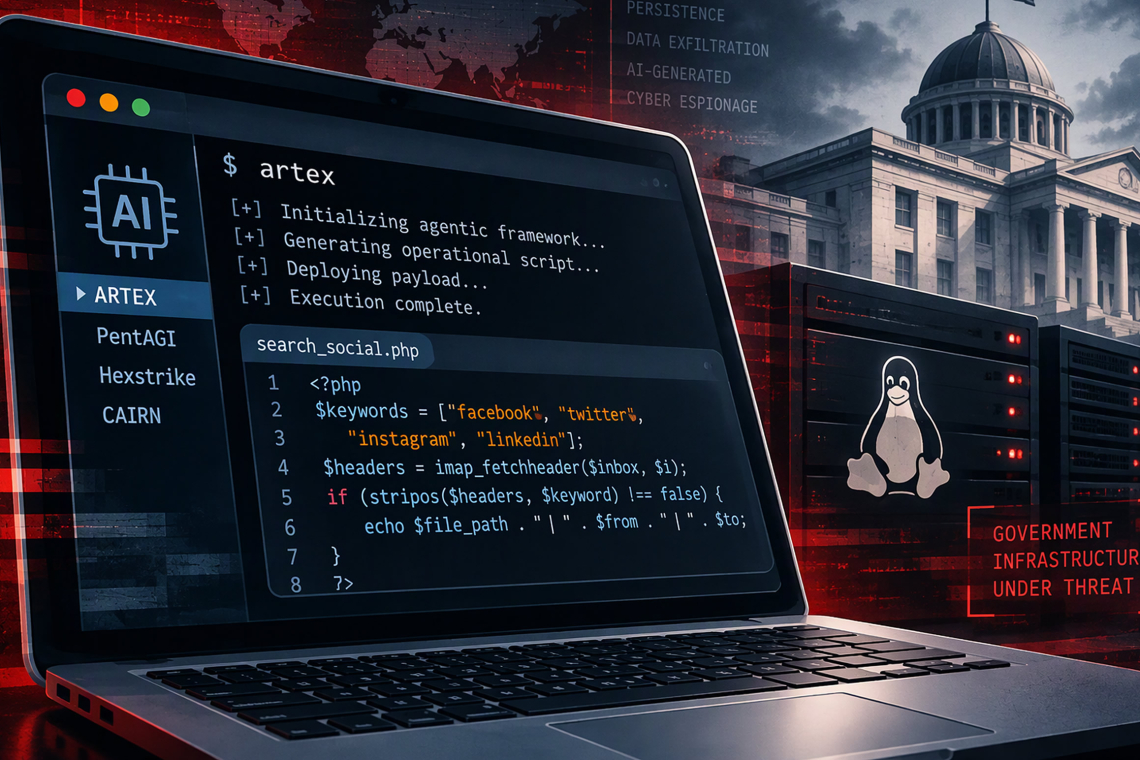
Investigators observed the deployment of a specialized PHP tool called search_social.php, which searched email repositories for references to social media platforms and accounts. The script extracted sender and recipient details, subject lines, and the exact location of matching email files, presenting the information in a format that streamlined intelligence collection.
The threat actors additionally attempted to deploy a Bash utility named zip_mails.sh, intended to compress and exfiltrate selected email archives. However, coding mistakes within the script caused it to fail during execution, providing another clue that portions of the operation may have been rapidly generated with limited human review.
Researchers assess that the campaign demonstrates a growing trend in which threat actors merge traditional post-exploitation techniques with AI-assisted development. By using AI tools to rapidly create, customize, and deploy malicious code, attackers can increase operational speed while reducing the need for manual programming effort.
The findings come amid broader industry warnings about the growing misuse of AI-powered offensive security frameworks. Security teams from Google Threat Intelligence Group (GTIG), Mandiant, and Microsoft recently reported increased abuse of agentic penetration-testing platforms such as ARTEX, PentAGI, Hexstrike, and CAIRN, which enable threat actors to automate large portions of the attack lifecycle at unprecedented scale.
Although the original ARTEX framework was withdrawn following reports of abuse, variants have continued to emerge, including a commercial edition known as ARTEX PRO and a localized derivative called ScopeWeaver.
Documented cases include ARTEX being used by cybercriminal and state-sponsored groups to automate reconnaissance, support data theft operations, conduct extortion campaigns, and accelerate attacks against organizations across sectors including enterprise software, industrial automation, semiconductor manufacturing, telecommunications, and financial services. North Korean-linked threat groups have also reportedly leveraged the framework in certain operations.
Security researchers warn that the rise of AI-driven offensive platforms signals a major evolution in cyber threats. While these tools enable attackers to dramatically shorten attack timelines and operate at machine speed, they often leave behind distinctive code patterns, behavioral artifacts, and network indicators that can increase the chances of detection and mitigation by defenders.
Found this article interesting? Follow us on X(Twitter) ,Threads and FaceBook to read more exclusive content we post.
