
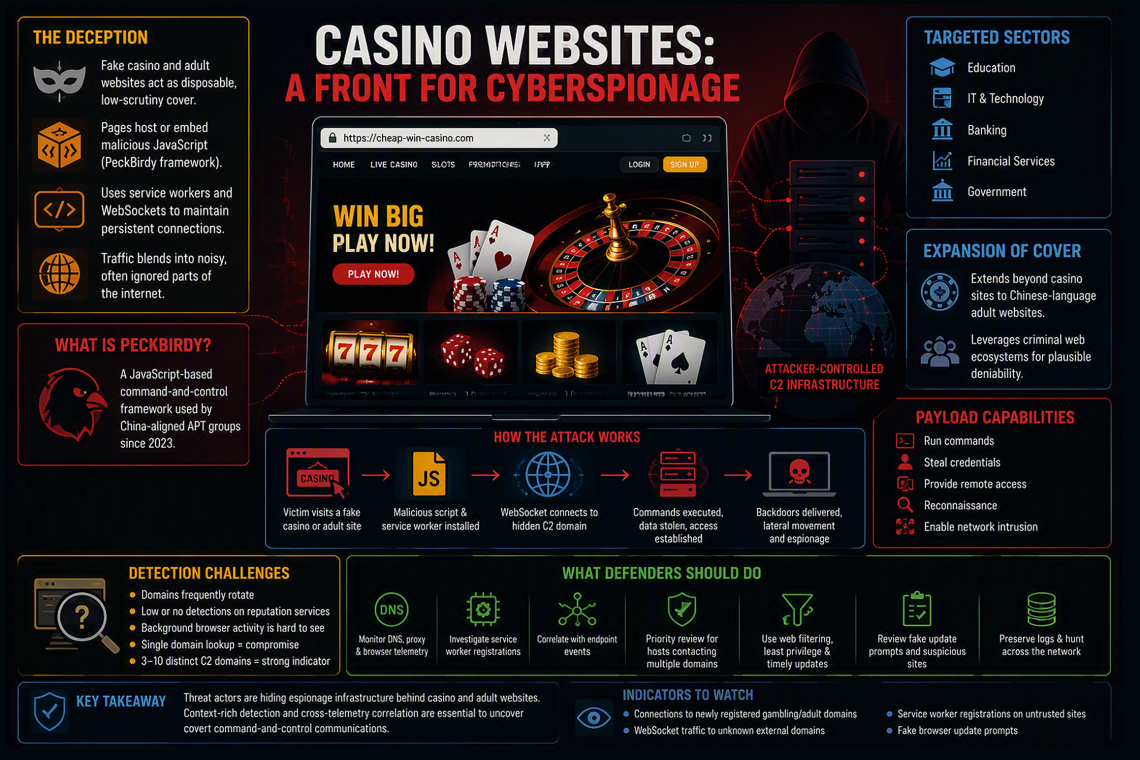
Cybersecurity researchers have uncovered a campaign in which seemingly harmless casino websites are being leveraged to hide infrastructure used for cyberespionage operations. While these sites appear to be low-quality gambling portals, some secretly facilitate communication between victims and attacker-controlled command-and-control (C2) servers.
Designed to look disposable and unremarkable, the websites often avoid attracting security scrutiny. At the center of the activity is PeckBirdy, a JavaScript-based command-and-control framework that has been used by China-aligned advanced persistent threat (APT) groups since 2023.
The campaigns have targeted government agencies and private-sector organizations across Asia, including entities in education, information technology, banking, financial services, and government sectors. Researchers at Infoblox uncovered the latest evolution of the campaign while investigating a large network of illicit gambling domains.
According to findings shared with Cyber Security News, threat actors have expanded beyond casino-themed websites and are now using Chinese-language adult websites as additional cover. This tactic highlights how espionage operators can exploit existing criminal web ecosystems to disguise their infrastructure and avoid detection.
Rather than relying on obvious malicious domains, attackers embed code within websites that appear insignificant. These pages can establish background browser connections, host malicious scripts, and conceal command-and-control traffic within a noisy and often-overlooked segment of the internet. As a result, defenders may focus on the visible lure while missing the hidden espionage activity occurring behind the scenes.
Espionage Infrastructure Hidden in Plain Sight
Researchers distinguish this activity from traditional casino-related cybercrime schemes such as illegal gambling operations, money-laundering platforms, or fraudulent betting websites designed to steal user deposits.
In the case of PeckBirdy, the casino website itself is merely a disguise. The gambling features are intended to provide legitimacy and camouflage rather than attract genuine players.
During their investigation, analysts identified a casino-themed webpage that registered a JavaScript service worker and loaded suspicious code bearing similarities to previously documented PeckBirdy deployments.
Service workers can operate in the background independently of active browser sessions, making them particularly useful for maintaining persistent communications after a user leaves a website. This capability can enable attackers to sustain covert interactions with compromised devices while minimizing visible indicators of compromise.
Researchers also discovered websites that concealed command servers behind familiar casino branding. Further analysis revealed active WebSocket connections communicating with separate domains, a pattern that was also observed on related adult-themed websites.
This multi-layered architecture makes detection significantly more difficult. Traditional reputation-based security controls and automated scanners may fail to identify malicious activity because much of the functionality occurs through browser-side scripts and background processes that are not immediately visible during basic inspections.
Additionally, PeckBirdy infrastructure has been linked to fake browser update campaigns that trick users into downloading malware. These fraudulent update prompts can ultimately deliver backdoors and other malicious tools that provide attackers with long-term access to compromised systems.
Security researchers note that the framework is associated with secondary payloads capable of:
- Executing remote commands
- Stealing user credentials
- Establishing persistent remote access
- Performing post-compromise reconnaissance
- Expanding intrusion activity across networks
This means a seemingly routine visit to a malicious website can potentially escalate into a broader enterprise compromise.
Detection Challenges and Security Risks
The report found that slightly more than three percent of monitored enterprise customers had resolved at least one PeckBirdy-related command-and-control domain.
While a single DNS lookup does not necessarily indicate a successful compromise, repeated communication with multiple PeckBirdy domains presents a much stronger indicator of malicious activity.
Researchers observed that systems resolving between three and ten distinct PeckBirdy command-and-control domains represented a significantly higher-risk scenario requiring immediate investigation.
Detection rates across security platforms also varied considerably. Some PeckBirdy-linked domains were identified by several threat intelligence engines, while others generated few detections or none at all. This inconsistency demonstrates the limitations of relying solely on domain reputation services when investigating sophisticated threat activity.
Because the infrastructure is intentionally designed to blend into commonly visited web services, clean reputation scores should not be treated as proof that a domain is safe.
Recommended Defensive Measures
Organizations should adopt a layered detection strategy rather than blocking individual domains as they appear. Threat actors frequently rotate domains, hosting providers, and supporting infrastructure, making domain-based blocking alone ineffective.
Security teams should:
- Monitor DNS, proxy, and browser activity for suspicious communications
- Investigate unusual service-worker registrations
- Correlate browser activity with endpoint telemetry
- Review hosts contacting multiple suspicious domains
- Preserve relevant logs for forensic analysis
- Examine potential exposure to fake browser update campaigns
- Monitor access to suspicious gambling and adult-themed websites
- Enforce least-privilege access controls
- Maintain updated browsers and endpoint protection tools
- Strengthen web-filtering controls across the organization
Key Takeaway
The PeckBirdy campaign demonstrates how threat actors are increasingly hiding cyberespionage infrastructure behind legitimate-looking web content. By blending malicious command-and-control operations into casino and adult websites, attackers can evade conventional detection methods and maintain covert access to target networks.
For defenders, effective detection requires correlating browser behavior, DNS activity, network communications, and endpoint telemetry. A broader, context-driven approach is essential to uncovering covert command-and-control channels that may appear indistinguishable from ordinary web traffic.
Found this article interesting? Follow us on X(Twitter) ,Threads and FaceBook to read more exclusive content we post.
