
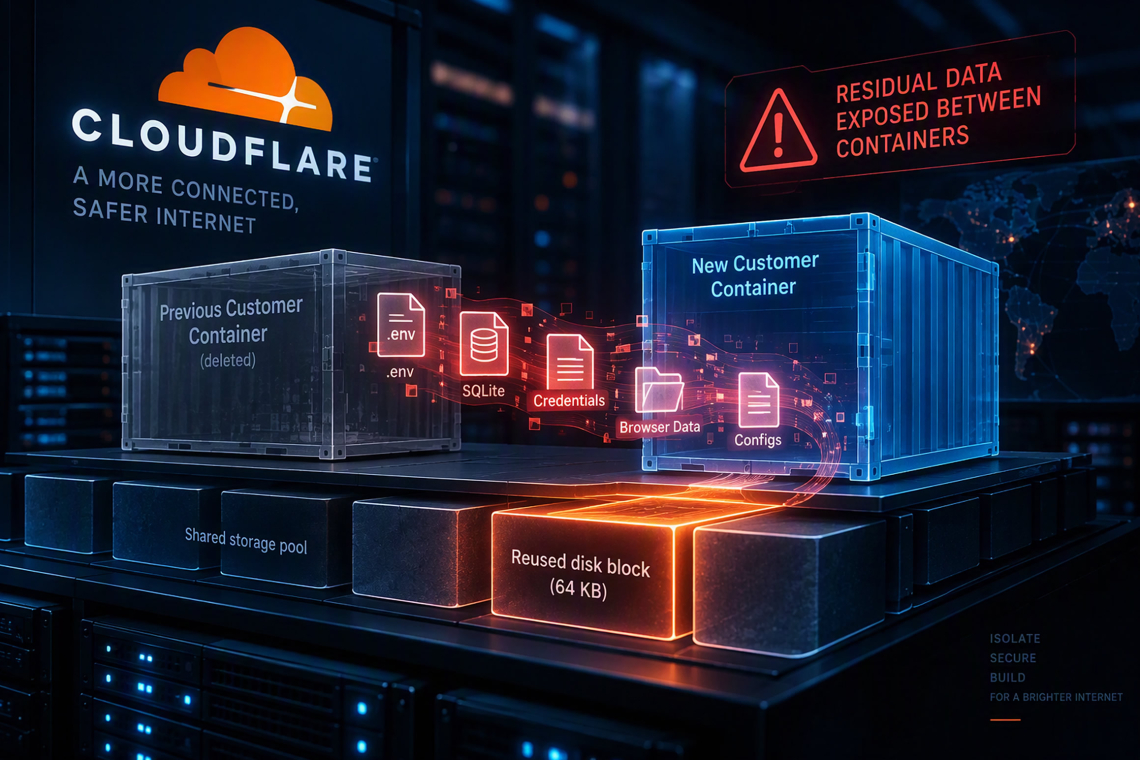
A recently disclosed security flaw in Cloudflare Containers allowed one customer’s container to access residual data left behind by other customers on the same physical server, according to details released jointly by the company and the researchers who discovered the issue.
The vulnerability did not expose information from active workloads. Instead, it involved remnants of data stored in disk blocks that had previously been used by other containers and later returned to a shared storage pool. While an attacker could potentially recover leftover information, they had no way to select a specific target customer. Cloudflare has since fully remediated the issue and stated that no customer action is required.
The affected service, Cloudflare Containers, operates by running customer applications in isolated containers across multi-tenant infrastructure, with server placement managed entirely by Cloudflare. The flaw also impacted Cloudflare Sandboxes, a service designed to safely execute untrusted workloads, including code generated by AI agents.
The vulnerability was reported on September 4 through Cloudflare's bug bounty program by security researcher Oren Yomtov of Accomplish.
At the heart of the issue was the platform's storage architecture. Container disks relied on a Linux storage mechanism known as thin provisioning, which allocates storage in 64 KB chunks. When containers were deleted, their associated storage blocks were returned to a shared pool that could later be reassigned to other customer environments.
Although such storage blocks are typically sanitized before reuse, the shared storage pool had been configured to bypass the block-wiping process. As a result, when a newly created container wrote only a small amount of data to a recycled block, the remainder of that block could still contain information from a previous tenant.
Researchers demonstrated the weakness by writing a small 4 KB payload into unallocated disk space and then reading the entire block at a low level. The untouched portion of the block, approximately 60 KB, frequently contained residual data belonging to earlier containers.
Testing revealed the issue was widespread. Across multiple production environments, researchers recovered leftover data in 18 out of 24 attempts and identified affected systems on 20 of 22 underlying servers spanning four continents.
According to Cloudflare, the recovered information included filesystem structures, database fragments, and complete SQLite databases. The researchers reported finding directory listings, Chromium browser profiles, environment configuration files (.env), credential-related files, and other artifacts associated with different customers' workloads.
Importantly, the researchers stated that their validation tools were designed to identify file formats and metadata rather than access or expose customer content. They also confirmed that any recovered artifacts were handled responsibly, never publicly disclosed, and securely deleted after being shared with Cloudflare for investigation.
The security team found no evidence that the flaw could be exploited to alter another customer's active data, interfere with running workloads, or cause service disruptions. The exposure was limited to reading residual information left behind in recycled storage blocks.
Cloudflare addressed the vulnerability through a two-phase remediation effort. The first step involved re-enabling automatic wiping of storage blocks before reassignment, immediately preventing further exploitation through the reported technique. Researchers later confirmed that their proof-of-concept attack no longer worked after this change was implemented.
However, the company determined that previously allocated storage blocks could still persist within active container disks and cached image layers. To eliminate any remaining risk, Cloudflare conducted a large-scale cleanup operation that retired active container disks, cleared storage caches, and restarted affected servers during maintenance windows. The remediation process concluded on September 19, with public disclosure following several days later.
As part of its investigation, Cloudflare developed detection mechanisms based on the researchers' proof-of-concept and analyzed retained storage activity logs for signs of abuse. The review identified only authorized testing performed by the reporting researchers and internal security engineers. The company stated that it found no evidence indicating that external threat actors had exploited the vulnerability.
The exact duration of potential exposure remains unclear, as Cloudflare did not disclose when the unsafe storage configuration was first introduced or how long it remained active before discovery.
The researchers also claimed that a similar storage configuration affected Browser Run, another Cloudflare offering. However, in its official disclosure, Cloudflare specifically identified only Containers and Sandboxes as impacted services.
Notably, the finding represents the sixth sandbox-escape or isolation-related vulnerability disclosed by the research team since July. Previous investigations uncovered comparable weaknesses affecting products from organizations including Anthropic, Claude Code, Claude Cowork, Cursor, Docker, and OpenAI's Codex, underscoring the growing security challenges surrounding modern containerized and AI-powered execution environments.
Found this article interesting? Follow us on X(Twitter) ,Threads and FaceBook to read more exclusive content we post.
