
Confidential computing platforms are intended to ensure that customer data remains protected, even from cloud or server administrators. However, a newly disclosed attack known as DDRop demonstrates that these security guarantees can be compromised when attackers gain the ability to manipulate the DDR5 memory communication channel.
Unlike traditional cyberattacks that rely on malware or software vulnerabilities, DDRop is a hardware-based attack that targets the memory subsystem. The technique has been shown to affect workloads protected by both Intel Trust Domain Extensions (TDX) and AMD Secure Encrypted Virtualization Secure Nested Paging (SEV-SNP).
Previous research had already highlighted potential weaknesses in confidential virtual machine environments. Earlier studies involving Intel TDX revealed that a malicious virtual machine manager could infer activity occurring inside a protected trust domain by monitoring behavioral patterns.
DDRop pushes the attack surface even deeper, bypassing software layers entirely and focusing on memory commands exchanged between the CPU and DDR5 memory modules.
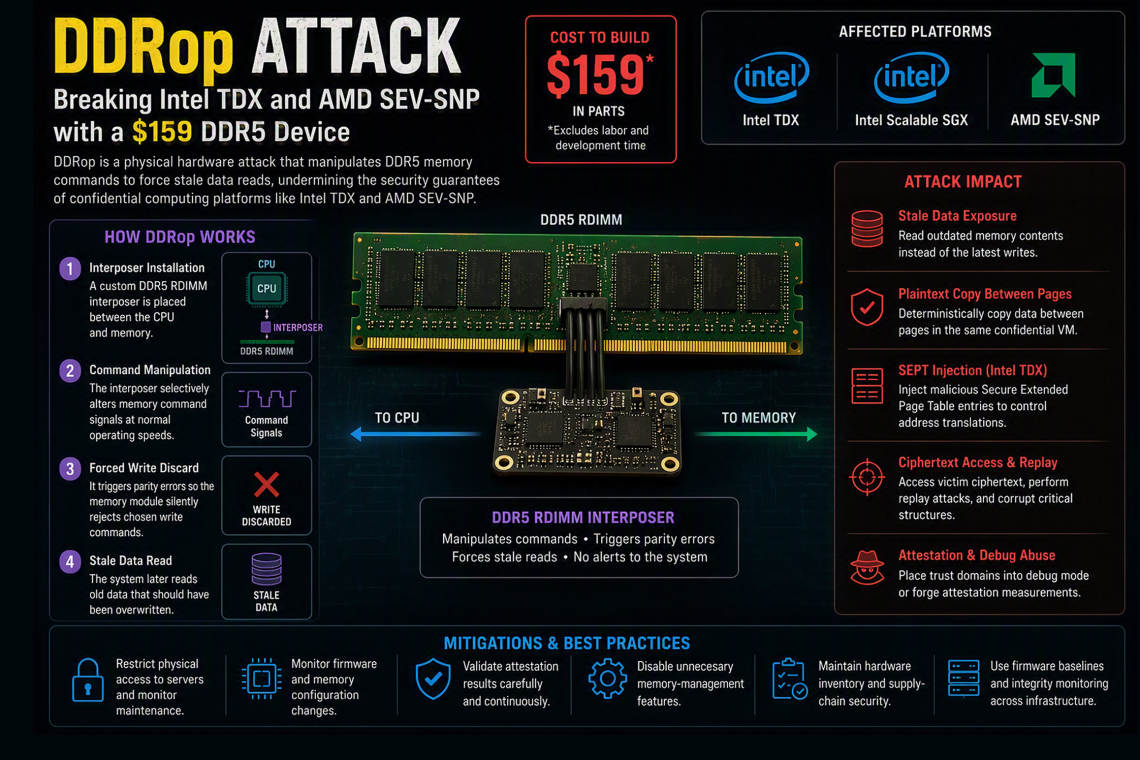
According to researchers who published the project's materials on GitHub, DDRop employs a custom-built DDR5 registered DIMM (RDIMM) interposer capable of manipulating memory write operations while the system continues to operate at normal speeds.
The research package includes hardware schematics, controller firmware, host-side utilities, and proof-of-concept exploit code for affected platforms. Successfully executing the attack requires administrative control of the target host system and short-term physical access to install the specialized hardware device.
Although these requirements make the attack impractical against typical end users, DDRop presents a significant concern for cloud providers, colocation facilities, and enterprise data centers where physical access may occur during maintenance activities, hardware servicing, or supply-chain processes.
How DDRop Works
Researchers reported that the attack hardware can be assembled for approximately $159, excluding labor and development expenses. The interposer is positioned between the processor and a DDR5 RDIMM module, enabling it to manipulate memory command signals rather than directly reading application data.
By deliberately triggering parity check failures, the device can cause selected memory write operations to be rejected by the memory module without generating appropriate system alerts.
As a result, intended memory updates may never occur. When a protected virtual machine later accesses that memory location, it may unknowingly retrieve older data that should have already been overwritten. This ability to force stale data reads forms the foundation of the DDRop attack.
Researchers determined that Intel TDX, Intel Scalable SGX, and AMD SEV-SNP are vulnerable because current scalable memory-encryption architectures do not always verify that encrypted memory contains the most recent version of stored data.
This distinction is crucial. While memory encryption prevents unauthorized parties from reading data, it does not inherently guarantee that the data is fresh, current, and resistant to replay or rollback attacks.
The findings echo concerns raised in previous DRAM-level security research, which showed that hardware manipulations occurring beneath the operating system can bypass protections that assume memory contents and addresses remain consistent.
Security Implications for TDX and SEV-SNP
The impact of DDRop becomes even more severe when combined with memory-management interfaces accessible to a malicious host.
Researchers demonstrated that attackers could interfere with page migration processes, causing destination memory pages to retain outdated information. During testing, this capability enabled reliable copying of plaintext data between pages belonging to the same confidential virtual machine.
In Intel TDX environments, researchers also succeeded in injecting malicious Secure Extended Page Table (SEPT) entries. Such manipulation can compromise protected address translations, potentially allowing attackers to access encrypted victim data, perform replay attacks, and corrupt critical control structures.
Additional proof-of-concept attacks showed that adversaries could force a trust domain into debug mode or falsify expected attestation measurements, thereby weakening trust guarantees provided by confidential computing environments.
Mitigation and Defensive Measures
Researchers noted that the most effective long-term solution will require future hardware designs that enforce both cryptographic integrity protection and robust freshness verification for memory contents.
Until stronger protections become available, organizations should adopt several defensive measures:
- Restrict and closely monitor physical access to server hardware.
- Track firmware modifications and memory configuration changes.
- Validate platform attestation results carefully.
- Disable unnecessary memory-management features where possible.
- Implement strict hardware inventory controls and supply-chain security practices.
- Maintain firmware baselines and system integrity monitoring across data center infrastructure.
These precautions can help reduce exposure to physical hardware attacks such as DDRop, particularly in cloud, AI, and enterprise data center environments where confidential computing technologies are increasingly relied upon to protect sensitive workloads.
Found this article interesting? Follow us on X(Twitter) ,Threads and FaceBook to read more exclusive content we post.
